
← Articles · Attack record · Poster
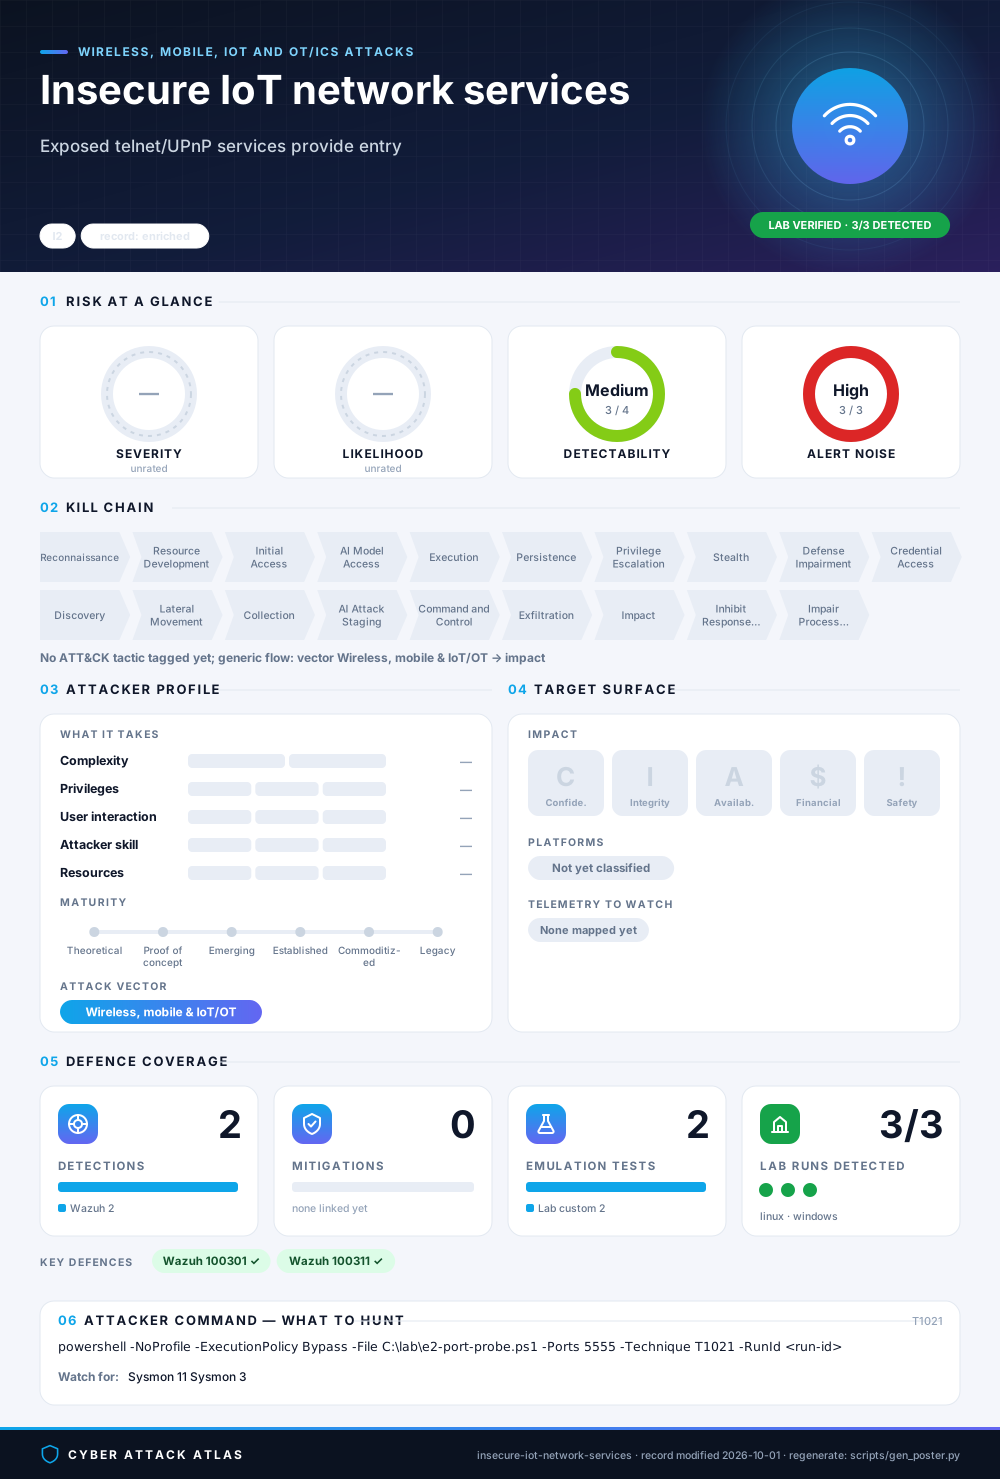
Insecure IoT network services
Exposed telnet/UPnP services provide entry
Overview
- Category: Wireless, mobile, IoT and OT/ICS attacks (
wireless-mobile-iot-ot) - Record status: enriched
Classification
Detection & telemetry
- detectability — Medium lab-2026-09-26
- noise level — High lab-2026-09-26
- testability — Custom lab test lab-2026-09-26
Detection & response
Detected by
100301(wazuh) — lab_detected=1 rule_level=7 alerts_expected=1 alerts_incidental=3 fp_per_hour=44.0 run=run-2026-09-28-001 lab-2026-09-28100311(wazuh) — lab_detected=1 rule_level=7 alerts_expected=1 alerts_incidental=5 fp_per_hour=122.0 run=run-2026-09-26-001 lab-2026-09-26
Tested by
lab-custom-e2-adb-probe(other) — run=run-2026-09-26-001 platform=linux elevation=1 outcome=detected lab-2026-09-26lab-custom-e2-adb-probe-win(other) — run=run-2026-09-28-001 platform=windows elevation=1 outcome=detected lab-2026-09-28
Lab findings
Measured in the isolated Phase 4 detection lab (Wazuh/Sysmon/auditd). Each run detonates a benign emulation of the attack's linchpin behaviour and grades what the SIEM saw.
| run | outcome | tool | platform | elev | ran at |
|---|---|---|---|---|---|
run-2026-09-26-001 | detected | other/e2-adb-probe | linux | yes | 2026-09-26 |
run-2026-09-28-001 | detected | other/e2-adb-probe-win | windows | yes | 2026-09-28 |
Run detail:
run-2026-09-26-001— E2 probe for Wazuh rule 100311 (Linux/auditd sibling of 100301; mobile-adjacent; the enterprise T1021 tag is what the manager's bundled MITRE DB can resolve). Same benign connect-only behaviour.; expected=1 incidental=5 max_level=7 dwell_s=90run-2026-09-28-001— E2 probe for Wazuh rule 100301 (the Windows/Sysmon sibling of 100311; mobile-adjacent). Same benign, connect-only behaviour as the Linux probe, but completes the connection so Sysmon EID 3 is emitted.; expected=1 incidental=3 max_level=15 dwell_s=90
Framework references
- Primary source: https://owasp.org/www-project-internet-of-things/
- owasp-iot: I2 (primary)
Evidence & sources
- ev-0001 (Cyber Attack Taxonomy (
Cyber-Attack-Taxonomy.md)) — Name, definition and Example/ID taken verbatim from the 'Wireless, mobile, IoT and OT/ICS attacks' table, line 497 of Cyber-Attack-Taxonomy.md - ev-0002 (Phase 4 detection lab - detonation runs 2026-09-26 (
lab/results/)) — Lab detonation run-2026-09-26-001 (detected): Wazuh rule(s) 100311 fired on T1021 within the detonation window > Mobile-adjacent (Linux): Android Debug Bridge (adb) connect() to TCP 5555, from auditd SOCKADDR. Mobile ref T1428. - ev-0003 (Phase 4 detection lab - detonation runs 2026-09-28 (
lab/results/)) — Lab detonation run-2026-09-28-001 (detected): Wazuh rule(s) 100301 fired on T1021 within the detonation window > Mobile-adjacent: Android Debug Bridge (adb) network connection on TCP 5555. Mobile ref T1428.
_Generated by scripts/gen_article.py from attacks.db (build 4b2db41c7733, 633 attacks). Source of truth: data/attacks/insecure-iot-network-services.yaml. Regenerate; do not hand-edit._