
← Articles · Attack record · Poster
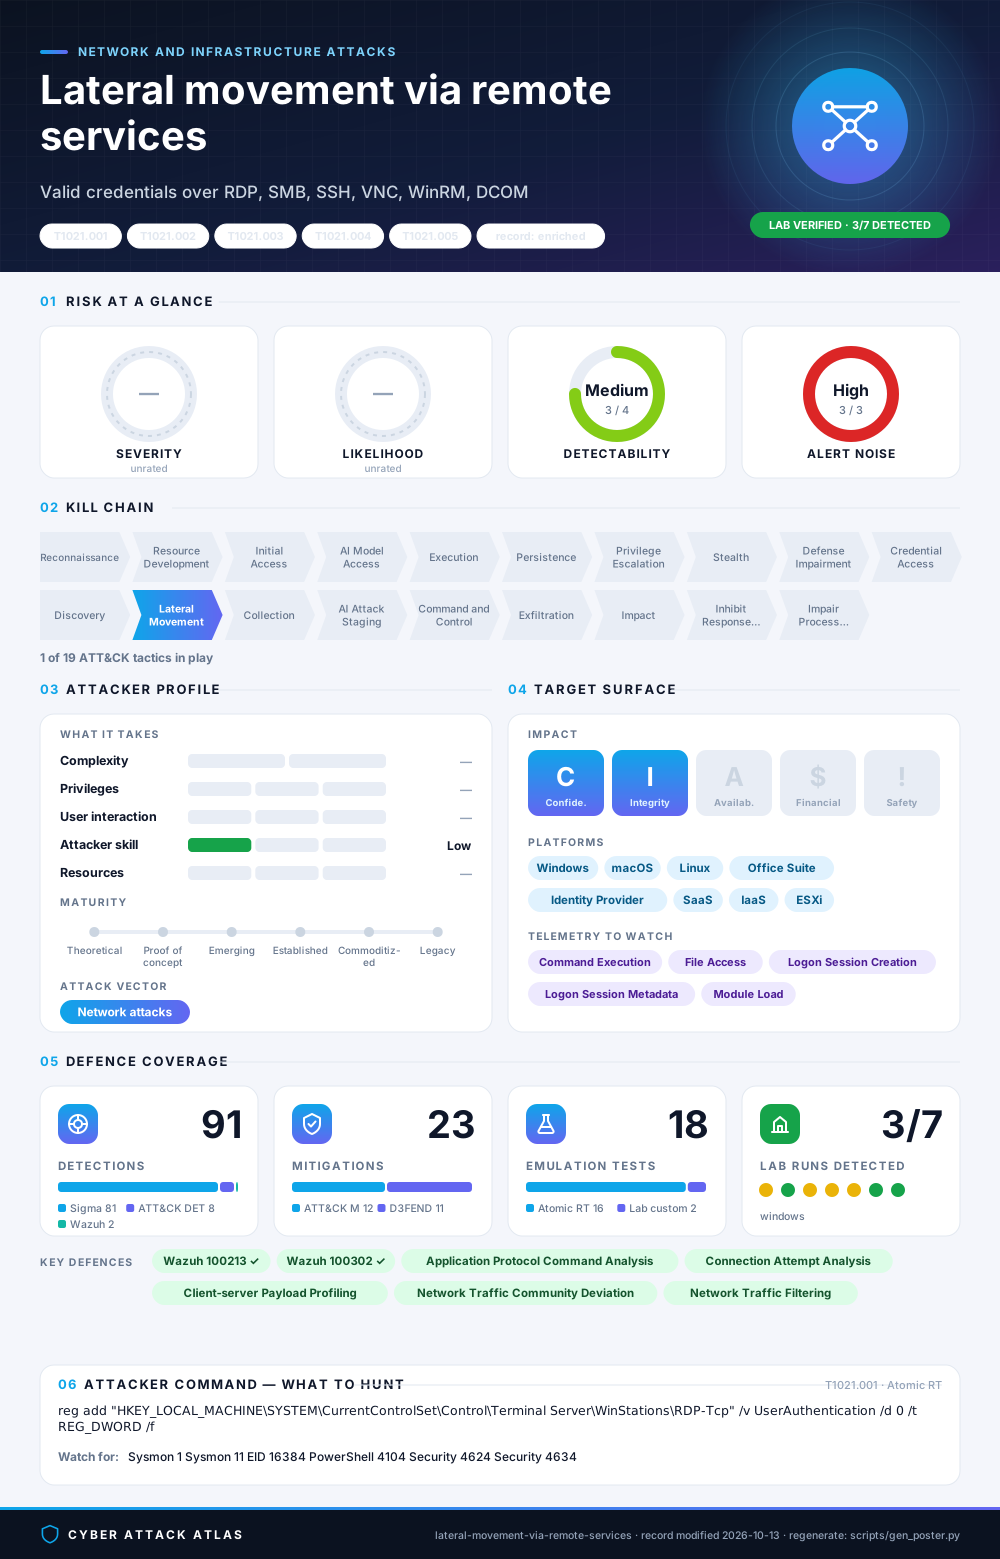
Lateral movement via remote services
Valid credentials over RDP, SMB, SSH, VNC, WinRM, DCOM
Overview
- Category: Network and infrastructure attacks (
network-infrastructure) - Record status: enriched
- Illustrative example: RDP in 66% of cases (Sophos)
Classification
Impact & scope
- platform — ESXi, IaaS, Identity Provider, Linux, Office Suite, SaaS, Windows, macOS mitre-attack-enterprise-19.2
- kill chain phase — Lateral Movement mitre-attack-enterprise-19.2
Detection & telemetry
- detectability — Medium lab-2026-09-30
- noise level — High lab-2026-09-30
- data sources — Command Execution, File Access, Logon Session Creation, Logon Session Metadata, Module Load, Network Connection Creation, Network Traffic Content, Network Traffic Flow, Process Creation, Service Metadata mitre-attack-enterprise-19.2
- testability — Atomic Red Team test, Custom lab test atomic-red-team-2026-09-18, lab-2026-09-30
Detection & response
Mitigated by
M1018(attack-mitigation) mitre-attack-enterprise-19.2M1026(attack-mitigation) mitre-attack-enterprise-19.2M1027(attack-mitigation) mitre-attack-enterprise-19.2M1028(attack-mitigation) mitre-attack-enterprise-19.2M1030(attack-mitigation) mitre-attack-enterprise-19.2M1032(attack-mitigation) mitre-attack-enterprise-19.2M1033(attack-mitigation) mitre-attack-enterprise-19.2M1035(attack-mitigation) mitre-attack-enterprise-19.2M1037(attack-mitigation) mitre-attack-enterprise-19.2M1042(attack-mitigation) mitre-attack-enterprise-19.2M1047(attack-mitigation) mitre-attack-enterprise-19.2M1048(attack-mitigation) mitre-attack-enterprise-19.2D3-APCA(d3fend) — Application Protocol Command Analysis [D3-APCA] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-CAA(d3fend) — Connection Attempt Analysis [D3-CAA] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-CSPP(d3fend) — Client-server Payload Profiling [D3-CSPP] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-NTCD(d3fend) — Network Traffic Community Deviation [D3-NTCD] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-NTF(d3fend) — Network Traffic Filtering [D3-NTF] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-NTSA(d3fend) — Network Traffic Signature Analysis [D3-NTSA] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-PHDURA(d3fend) — Per Host Download-Upload Ratio Analysis [D3-PHDURA] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-PMAD(d3fend) — Protocol Metadata Anomaly Detection [D3-PMAD] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-RTSD(d3fend) — Remote Terminal Session Detection [D3-RTSD] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-ST(d3fend) — Session Termination [D3-ST] counters ATT&CK T1021.001, T1021.004 (D3FEND 1.6.0) mitre-d3fend-1.6.0D3-UGLPA(d3fend) — User Geolocation Logon Pattern Analysis [D3-UGLPA] counters ATT&CK T1021.001, T1021.002, T1021.003, T1021.004, T1021.005, T1021.006, T1021.007, T1021.008 (D3FEND 1.6.0) mitre-d3fend-1.6.0
Detected by
DET0008(attack-detection-strategy) mitre-attack-enterprise-19.2DET0178(attack-detection-strategy) mitre-attack-enterprise-19.2DET0211(attack-detection-strategy) mitre-attack-enterprise-19.2DET0285(attack-detection-strategy) mitre-attack-enterprise-19.2DET0327(attack-detection-strategy) mitre-attack-enterprise-19.2DET0477(attack-detection-strategy) mitre-attack-enterprise-19.2DET0530(attack-detection-strategy) mitre-attack-enterprise-19.2DET0596(attack-detection-strategy) mitre-attack-enterprise-19.2021310d9-30a6-480a-84b7-eaa69aeb92bb(sigma) sigma-rules-2026-09-18055fb54c-a8f4-4aee-bd44-f74cf30a0d9d(sigma) sigma-rules-2026-09-1805a2ab7e-ce11-4b63-86db-ab32e763e11d(sigma) sigma-rules-2026-09-18098d7118-55bc-4912-a836-dc6483a8d150(sigma) sigma-rules-2026-09-180d5675be-bc88-4172-86d3-1e96a4476536(sigma) sigma-rules-2026-09-1810c14723-61c7-4c75-92ca-9af245723ad2(sigma) sigma-rules-2026-09-1816ab6143-510a-44e2-a615-bdb80b8317fc(sigma) sigma-rules-2026-09-18183e7ea8-ac4b-4c23-9aec-b3dac4e401ac(sigma) sigma-rules-2026-09-181c563233-030e-4a07-af8c-ee0490a66d3a(sigma) sigma-rules-2026-09-181fc0809e-06bf-4de3-ad52-25e5263b7623(sigma) sigma-rules-2026-09-18214e8f95-100a-4e04-bb31-ef6cba8ce07e(sigma) sigma-rules-2026-09-182f7979ae-f82b-45af-ac1d-2b10e93b0baa(sigma) sigma-rules-2026-09-182f974656-6d83-4059-bbdf-68ac5403422f(sigma) sigma-rules-2026-09-18327f48c1-a6db-4eb8-875a-f6981f1b0183(sigma) sigma-rules-2026-09-1832d56ea1-417f-44ff-822b-882873f5f43b(sigma) sigma-rules-2026-09-183abd6094-7027-475f-9630-8ab9be7b9725(sigma) sigma-rules-2026-09-183ce8e9a4-bc61-4c9b-8e69-d7e2492a8781(sigma) sigma-rules-2026-09-1845545954-4016-43c6-855e-eae8f1c369dc(sigma) sigma-rules-2026-09-1848a61b29-389f-4032-b317-b30de6b95314(sigma) sigma-rules-2026-09-184b8f6d3a-9c5e-4f2a-a7d8-6b9c3e5f2a8d(sigma) sigma-rules-2026-09-1851e33403-2a37-4d66-a574-1fda1782cc31(sigma) sigma-rules-2026-09-1852a85084-6989-40c3-8f32-091e12e13f09(sigma) sigma-rules-2026-09-1852d8b0c6-53d6-439a-9e41-52ad442ad9ad(sigma) sigma-rules-2026-09-18551d9c1f-816c-445b-a7a6-7a3864720d60(sigma) sigma-rules-2026-09-18586a8d6b-6bfe-4ad9-9d78-888cd2fe50c3(sigma) sigma-rules-2026-09-18598290cf-5932-45cd-9123-be1e05ab4f2e(sigma) sigma-rules-2026-09-185a105d34-05fc-401e-8553-272b45c1522d(sigma) sigma-rules-2026-09-185bb68627-3198-40ca-b458-49f973db8752(sigma) sigma-rules-2026-09-185bed80b6-b3e8-428e-a3ae-d3c757589e41(sigma) sigma-rules-2026-09-185cdb711b-5740-4fb2-ba88-f7945027afac(sigma) sigma-rules-2026-09-185f699bc5-5446-4a4a-a0b7-5ef2885a3eb4(sigma) sigma-rules-2026-09-1860167e5c-84b2-4c95-a7ac-86281f27c445(sigma) sigma-rules-2026-09-18614a7e17-5643-4d89-b6fe-f9df1a79641c(sigma) sigma-rules-2026-09-1861a7697c-cb79-42a8-a2ff-5f0cdfae0130(sigma) sigma-rules-2026-09-1868050b10-e477-4377-a99b-3721b422d6ef(sigma) sigma-rules-2026-09-186e8fe0a8-ba0b-4a93-8f9e-82657e7a5984(sigma) sigma-rules-2026-09-186fb63b40-e02a-403e-9ffd-3bcc1d749442(sigma) sigma-rules-2026-09-1872124974-a68b-4366-b990-d30e0b2a190d(sigma) sigma-rules-2026-09-18734f8d9b-42b8-41b2-bcf5-abaf49d5a3c8(sigma) sigma-rules-2026-09-187707a579-e0d8-4886-a853-ce47e4575aaa(sigma) sigma-rules-2026-09-1878f10490-f2f4-4d19-a75b-4e0683bf3b8d(sigma) sigma-rules-2026-09-1879df3f68-dccb-48e9-9171-b75cbc37c51d(sigma) sigma-rules-2026-09-187b836d7f-179c-4ba4-90a7-a7e60afb48e6(sigma) sigma-rules-2026-09-187e6237fe-3ddb-438f-9381-9bf9de5af8d0(sigma) sigma-rules-2026-09-187f3a9c2d-4e8b-4a7f-9d3e-5c6f8a9b2e1d(sigma) sigma-rules-2026-09-18855bc8b5-2ae8-402e-a9ed-b889e6df1900(sigma) sigma-rules-2026-09-18871b9555-69ca-4993-99d3-35a59f9f3599(sigma) sigma-rules-2026-09-188d91f6e4-9f3b-4c21-ae41-2c5b7d9f7a12(sigma) sigma-rules-2026-09-188e5c03fa-b7f0-11ea-b242-07e0576828d9(sigma) sigma-rules-2026-09-18954f0af7-62dd-418f-b3df-a84bc2c7a774(sigma) sigma-rules-2026-09-1896b9f619-aa91-478f-bacb-c3e50f8df575(sigma) sigma-rules-2026-09-18991a9744-f2f0-44f2-bd33-9092eba17dc3(sigma) sigma-rules-2026-09-189f38c1db-e2ae-40bf-81d0-5b68f73fb512(sigma) sigma-rules-2026-09-18a197e378-d31b-41c0-9635-cfdf1c1bb423(sigma) sigma-rules-2026-09-18aa35a627-33fb-4d04-a165-d33b4afca3e8(sigma) sigma-rules-2026-09-18ab6b1a39-a9ee-4ab4-b075-e83acf6e346b(sigma) sigma-rules-2026-09-18ad1f4bb9-8dfb-4765-adb6-2a7cfb6c0f94(sigma) sigma-rules-2026-09-18b1e5da3b-ca8e-4adf-915c-9921f3d85481(sigma) sigma-rules-2026-09-18b210394c-ba12-4f89-9117-44a2464b9511(sigma) sigma-rules-2026-09-18bae2865c-5565-470d-b505-9496c87d0c30(sigma) sigma-rules-2026-09-18bcfece3d-56fe-4545-9931-3b8e92927db1(sigma) sigma-rules-2026-09-18c39f0c81-7348-4965-ab27-2fde35a1b641(sigma) sigma-rules-2026-09-18c462f537-a1e3-41a6-b5fc-b2c2cef9bf82(sigma) sigma-rules-2026-09-18c539afac-c12a-46ed-b1bd-5a5567c9f045(sigma) sigma-rules-2026-09-18c601f20d-570a-4cde-a7d6-e17f99cb8e7f(sigma) sigma-rules-2026-09-18d36f87ea-c403-44d2-aa79-1a0ac7c24456(sigma) sigma-rules-2026-09-18d3f90469-fb05-42ce-b67d-0fded91bbef3(sigma) sigma-rules-2026-09-18d4498716-1d52-438f-8084-4a603157d131(sigma) sigma-rules-2026-09-18d7a95147-145f-4678-b85d-d1ff4a3bb3f6(sigma) sigma-rules-2026-09-18df9a0e0e-fedb-4d6c-8668-d765dfc92aa7(sigma) sigma-rules-2026-09-18ed74fe75-7594-4b4b-ae38-e38e3fd2eb23(sigma) sigma-rules-2026-09-18efc21479-9e83-41da-8cf1-122e06ba8db3(sigma) sigma-rules-2026-09-18f117933c-980c-4f78-b384-e3d838111165(sigma) sigma-rules-2026-09-18f1b3a22a-45e6-4004-afb5-4291f9c21166(sigma) sigma-rules-2026-09-18f1f3bf22-deb2-418d-8cce-e1a45e46a5bd(sigma) sigma-rules-2026-09-18f318b911-ea88-43f4-9281-0de23ede628e(sigma) sigma-rules-2026-09-18f354eba5-623b-450f-b073-0b5b2773b6aa(sigma) sigma-rules-2026-09-18f6c68d5f-e101-4b86-8c84-7d96851fd65c(sigma) sigma-rules-2026-09-18f72aa3e8-49f9-4c7d-bd74-f8ab84ff9bbb(sigma) sigma-rules-2026-09-18f8103686-e3e8-46f3-be72-65f7fcb4aa53(sigma) sigma-rules-2026-09-18ffa28e60-bdb1-46e0-9f82-05f7a61cc06e(sigma) sigma-rules-2026-09-18100302(wazuh) — lab_detected=1 rule_level=7 alerts_expected=1 alerts_incidental=3 fp_per_hour=12.0 run=run-2026-09-30-002 lab-2026-09-30
Tested by
01d1c6c0-faf0-408e-b368-752a02285cb2(atomic) atomic-red-team-2026-09-180eb03d41-79e4-4393-8e57-6344856be1cf(atomic) atomic-red-team-2026-09-18280812c8-4dae-43e9-a74e-1d08ab997c0e(atomic) atomic-red-team-2026-09-182f840dd4-8a2e-4f44-beb3-6b2399ea3771(atomic) atomic-red-team-2026-09-183386975b-367a-4fbb-9d77-4dcf3639ffd3(atomic) atomic-red-team-2026-09-18355d4632-8cb9-449d-91ce-b566d0253d3e(atomic) atomic-red-team-2026-09-18505f24be-1c11-4694-b614-e01ae1cd2570(atomic) atomic-red-team-2026-09-18514e9cd7-9207-4882-98b1-c8f791bae3c5(atomic) atomic-red-team-2026-09-185295bd61-bd7e-4744-9d52-85962a4cf2d6(atomic) atomic-red-team-2026-09-186dc74eb1-c9d6-4c53-b3b5-6f50ae339673(atomic) atomic-red-team-2026-09-1874ace21e-a31c-4f7d-b540-53e4eb6d1f73(atomic) atomic-red-team-2026-09-188a930abe-841c-4d4f-a877-72e9fe90b9ea(atomic) atomic-red-team-2026-09-188f6c14d1-f13d-4616-b7fc-98cc69fe56ec(atomic) atomic-red-team-2026-09-189059e8de-3d7d-4954-a322-46161880b9cf(atomic) atomic-red-team-2026-09-18d41aaab5-bdfe-431d-a3d5-c29e9136ff46(atomic) atomic-red-team-2026-09-18efe86d95-44c4-4509-ae42-7bfd9d1f5b3d(atomic) atomic-red-team-2026-09-18lab-custom-e2-ssh-evasion-2222(other) — run=run-2026-09-30-003 platform=windows elevation=1 outcome=partially-detected lab-2026-09-30lab-custom-e2-ssh-probe-win(other) — run=run-2026-09-30-001 platform=windows elevation=1 outcome=partially-detected lab-2026-09-30
Lab findings
Measured in the isolated Phase 4 detection lab (Wazuh/Sysmon/auditd). Each run detonates a benign emulation of the attack's linchpin behaviour and grades what the SIEM saw.
| run | outcome | tool | platform | elev | ran at |
|---|---|---|---|---|---|
run-2026-09-30-001 | partially-detected | other/e2-ssh-probe-win | windows | yes | 2026-09-30 |
run-2026-09-30-002 | detected | other/e2-ssh-probe-win | windows | yes | 2026-09-30 |
run-2026-09-30-003 | partially-detected | other/e2-ssh-evasion-2222 | windows | yes | 2026-09-30 |
Run detail:
run-2026-09-30-001— E2 probe for CANDIDATE rule 100302 (Windows/Sysmon T1021.004: outbound SSH). Connects to a listener on lin-victim 10.10.10.22:22 (its sshd already listens there; if the connect is refused, start custom/e2-sink.py on port 22) so Sysmon EID 3 fires on a real established connection — connect-only, no auth, no payload, closed immediately. Benign. Measures the T1021.004 Windows gap BEFORE 100302 is deployed (expect not-detected / expected-but-silent 100302), then confirms detection after the rule is deployed.; expected=0 incidental=3 max_level=15 dwell_s=90run-2026-09-30-002— E2 probe for CANDIDATE rule 100302 (Windows/Sysmon T1021.004: outbound SSH). Connects to a listener on lin-victim 10.10.10.22:22 (its sshd already listens there; if the connect is refused, start custom/e2-sink.py on port 22) so Sysmon EID 3 fires on a real established connection — connect-only, no auth, no payload, closed immediately. Benign. Measures the T1021.004 Windows gap BEFORE 100302 is deployed (expect not-detected / expected-but-silent 100302), then confirms detection after the rule is deployed.; expected=1 incidental=3 max_level=15 dwell_s=90run-2026-09-30-003— Control-bypass variant of t1021.004-custom-windows-ssh (Phase 8.4). Identical benign SSH connect, but to TCP 2222 instead of 22. Rule 100302 matches destinationPort ^22$ exactly, so moving the port evades it while the lateral-movement behaviour is unchanged — a novel variant, so its detonation is G1 (human-gated). Expect NOT-detected (the evasion succeeds): the detection delta vs the port-22 baseline (run-2026-09-30-002, detected) is measured by agents/evasion.py. Connect to a listener on 10.10.10.22:2222 — start custom/e2-sink.py on 2222 (>1024, no sudo). Benign, connect-only, no auth, no payload.; expected=0 incidental=6 max_level=15 dwell_s=90
Framework references
- Primary source: https://attack.mitre.org/techniques/T1021/
- attack: T1021.001 (primary)
- attack: T1021.002
- attack: T1021.003
- attack: T1021.004
- attack: T1021.005
- attack: T1021.006
- attack: T1021.007
- attack: T1021.008
Evidence & sources
- ev-0001 (Cyber Attack Taxonomy (
Cyber-Attack-Taxonomy.md)) — Name, definition and Example/ID taken verbatim from the 'Network and infrastructure attacks' table, line 198 of Cyber-Attack-Taxonomy.md - ev-0002 (MITRE Enterprise ATT&CK v19.2 (STIX 2.1)) — ATT&CK usage prevalence: 10 groups/software/campaigns reference this technique (ATT&CK enterprise v19.2)
- ev-0003 (MITRE Enterprise ATT&CK v19.2 (STIX 2.1)) — ATT&CK usage prevalence: 11 groups/software/campaigns reference this technique (ATT&CK enterprise v19.2)
- ev-0004 (MITRE Enterprise ATT&CK v19.2 (STIX 2.1)) — ATT&CK usage prevalence: 27 groups/software/campaigns reference this technique (ATT&CK enterprise v19.2)
- ev-0005 (MITRE Enterprise ATT&CK v19.2 (STIX 2.1)) — ATT&CK usage prevalence: 3 groups/software/campaigns reference this technique (ATT&CK enterprise v19.2)
- ev-0006 (MITRE Enterprise ATT&CK v19.2 (STIX 2.1)) — ATT&CK usage prevalence: 5 groups/software/campaigns reference this technique (ATT&CK enterprise v19.2)
- ev-0007 (MITRE Enterprise ATT&CK v19.2 (STIX 2.1)) — ATT&CK usage prevalence: 63 groups/software/campaigns reference this technique (ATT&CK enterprise v19.2)
- ev-0008 (MITRE Enterprise ATT&CK v19.2 (STIX 2.1)) — ATT&CK usage prevalence: 65 groups/software/campaigns reference this technique (ATT&CK enterprise v19.2)
- ev-0009 (Phase 4 detection lab - detonation runs 2026-09-30 (
lab/results/)) — Lab detonation run-2026-09-30-001 (partially-detected) for T1021.004: no alert matched the expected technique - ev-0010 (Phase 4 detection lab - detonation runs 2026-09-30 (
lab/results/)) — Lab detonation run-2026-09-30-002 (detected): Wazuh rule(s) 100302 fired on T1021.004 within the detonation window > Lateral-movement-adjacent (Windows): outbound SSH connection on TCP 22. ATT&CK T1021.004 (Remote Services: SSH). - ev-0011 (Phase 4 detection lab - detonation runs 2026-09-30 (
lab/results/)) — Lab detonation run-2026-09-30-003 (partially-detected) for T1021.004: no alert matched the expected technique
_Generated by scripts/gen_article.py from attacks.db (build c436f5e9672b, 633 attacks). Source of truth: data/attacks/lateral-movement-via-remote-services.yaml. Regenerate; do not hand-edit._